This free Data Processing Agreement Template is built for SaaS companies — with a section most templates skip entirely: an AI Processing Addendum covering AI vendors, model training, and AI-generated output.
Download the free template → (.docx, no email required)
What makes this different
Most DPA templates online are generic — written once, years ago, for any company handling any kind of data. Many general-purpose DPA templates do not address the AI-specific questions SaaS companies increasingly face, such as whether an AI vendor may use customer data for model training.
This template covers both: the full set of GDPR Article 28 requirements every DPA needs, plus a dedicated AI Processing Addendum that closes the AI-specific gap.
It works in both directions
You’ll need a signed DPA in two different situations, and this one template handles both:
- As the Controller — when you’re bringing on a new vendor (a CRM, an AI tool, a cloud provider) that will process your data, you send them this DPA to sign.
- As the Processor — when your own SaaS product processes data on behalf of your customers, your customers will often ask you to sign a DPA. You can use the same template, just reversing which company fills in which role.
Fill in your own company as whichever party applies, and the agreement works the same either way.
What’s Inside This Data Processing Agreement Template
The core agreement covers everything GDPR Article 28(3) requires: processing only on documented instructions, confidentiality, security measures, sub-processor authorization, assistance with data subject rights, breach notification, audit rights, and data return or deletion at the end of the relationship — plus sections on international data transfers (with Standard Contractual Clauses language), liability, and term.
The requirements are based on Article 28 of the GDPR , which sets out the obligations for contracts between controllers and processors.
Annex A — Details of Processing — a fill-in table for subject matter, duration, data types, and data subjects, so the scope of the agreement is spelled out rather than left vague.
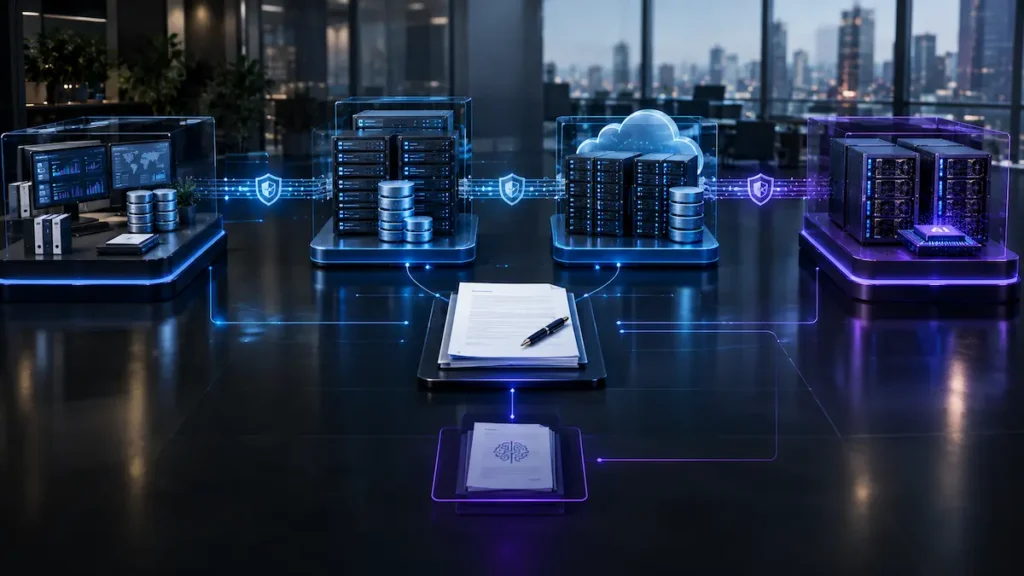
Annex B — Authorized Sub-processors — a tracking table for every vendor processing data on your behalf, including a dedicated row pattern for AI vendors.
Annex C — Technical and Organizational Security Measures — a checklist covering encryption, access control, monitoring, and incident response, matching what Article 32 actually requires. For the underlying security requirement, see Article 32 of the GDPR, which addresses the security of processing.
Annex D — AI Processing Addendum — the part no other free template includes:
- No training on your data without explicit written consent
- Disclosure of every AI system and underlying foundation model in use
- AI-generated output treated as personal data, with the same protections as the data it came from
- Human oversight requirements for any AI-assisted decision with real consequences for a person
- A path to request removal if your data ends up in training data improperly
Who this is for
SaaS companies — especially ones with at least one vendor relationship involving an AI tool, or ones whose own product uses AI to process customer data. If you’ve already run vendors through the Vendor Risk Assessment Workbook, this DPA is the natural next step for any vendor flagged as a Processor there.
How to use it
- Decide which direction applies — are you the Controller (bringing on a vendor) or the Processor (your customer is asking you to sign)?
- Fill in both parties’ details and replace the bracketed placeholders throughout.
- Complete Annex A with the actual scope of processing.
- List every sub-processor in Annex B, including any AI vendors.
- Complete Annex D if an AI system is involved anywhere in the processing — otherwise mark it “Not Applicable.”
- Route the final draft through your own legal counsel before signature. This template is a starting point, not legal advice.
Related resources
- AI Vendor Risk Assessment — the methodology for deciding which vendors need a DPA in the first place
- Vendor Risk Assessment Workbook — tracks DPA status for every vendor, tab by tab
- AI Policy Template — the broader governance policy this DPA supports
- ISO 42001 for SaaS — how DPA documentation connects to Annex A.10
- Spain GDPR Checklist for SaaS — the underlying GDPR detail