ISO 42001 for SaaS companies is increasingly appearing in conversations about AI governance, enterprise procurement, and due diligence as buyers look for evidence that AI is governed rather than simply marketed as “responsible.” Published in December 2023, it’s the first international standard for an AI management system.
Many ISO 42001 guides start from the assumption that certification means building an AI governance programme from scratch. If you’ve already built an AI policy, run a vendor risk assessment, or completed a DPIA, you’re likely starting with useful governance foundations already in place. This guide starts from that position.
Quick answer: ISO/IEC 42001 is a voluntary international standard for establishing, implementing, maintaining, and continually improving an AI Management System (AIMS). It is different from SOC 2 and does not replace obligations under laws such as the EU AI Act or GDPR. For a SaaS company, whether certification makes sense depends on customer requirements, AI risk, organizational scope, existing governance maturity, and the business value of independent certification.
What ISO 42001 Certification Actually Covers
An AI Management System, or AIMS, is the structured set of policies, processes, and controls an organization uses to govern how it develops, provides, or uses AI. ISO specifies that 42001 sets requirements for establishing, implementing, maintaining, and continually improving an AIMS — certification is a third-party conformity assessment against that standard, not a technical audit of any single model, using the same “Plan-Do-Check-Act” continuous-improvement structure common to other ISO management standards.
ISO/IEC 42001 itself is voluntary; a particular customer, contract, procurement requirement, sectoral framework, or other business arrangement may nevertheless make certification commercially necessary for a specific organization. What’s changing is the way some enterprise buyers, procurement teams, and due-diligence processes evaluate AI governance — as more SaaS products embed AI features, some of those processes are starting to ask for independent evidence of governance the way they’ve long asked for SOC 2 reports.
ISO 42001 vs. SOC 2 vs. EU AI Act vs. GDPR
These four get conflated constantly, and they’re solving different problems:
| ISO 42001 | SOC 2 | EU AI Act | GDPR | |
|---|---|---|---|---|
| What it is | Voluntary international certification | Voluntary attestation framework originating in the US | Binding EU law | Binding EU law |
| What it covers | An organization’s AI management system | Defined controls: security, availability, confidentiality | Risk-based obligations for AI providers and deployers | Personal data processing |
| Mandatory? | No, though contracts or procurement may effectively require it | No | Yes, for in-scope activities | Yes, for in-scope processing |
| Who assesses it | Independent certification body | Independent CPA firm | Self-assessed, with regulatory enforcement | Self-assessed, with regulatory enforcement |
| Best paired with | An AI product or heavy internal AI use | Any SaaS company handling customer data | Organizations with AI systems or activities within the Act’s scope | Organizations whose processing falls within the GDPR’s scope |
They’re complementary, not substitutes. A SOC 2 report addresses defined controls such as security, availability, and confidentiality. ISO/IEC 42001 establishes an AI management system. The EU AI Act is binding legislation with its own obligations based on the role of the organization and the type of AI system involved. ISO 42001 can provide useful governance structure and supporting evidence, but it does not by itself establish compliance with the EU AI Act — the European Commission has specifically noted that ISO/IEC 42001’s goals and definitions aren’t aligned with the quality management system the Act requires, and that harmonized AI Act-specific standards are being developed separately.
For EU-facing companies: don’t treat ISO 42001 certification as a shortcut around AI Act conformity, documentation, risk-management, or other applicable obligations. Use it as supporting governance infrastructure, not a substitute for legal analysis.
ISO 42001 Alignment vs. Certification
It’s worth separating two things people often collapse into one:
Alignment (or readiness) means you’ve designed and operate governance processes against the standard’s requirements — you’re following the structure without a certification body having audited you against it.
Certification means an independent certification body has audited your AIMS against ISO/IEC 42001 and issued certification within a defined scope. Certification bodies conducting ISO/IEC 42001 audits are subject to the additional requirements specified in ISO/IEC 42006:2025, which addresses the competence and consistency of bodies performing AIMS audits and certification.
A startup can use ISO 42001 as a governance framework — building the policy, risk-management, and oversight structure it describes — well before deciding whether third-party certification provides enough commercial value to justify the audit. For many early-stage companies, alignment is the more immediately useful goal; certification becomes worth pursuing once a specific customer, deal, or diligence process asks for it.
Do You Need ISO 42001 Yet?
Certification isn’t free — expect real cost and real time (see the breakdown below) — so it’s worth being honest about whether now is the right moment. Consider pursuing it when:
- An enterprise customer or a specific RFP has explicitly asked for it
- You’re in a diligence process where AI-governance questions are coming up repeatedly
- Your AI systems support higher-impact use cases (hiring, credit, health, safety) where stronger governance evidence may be commercially or operationally valuable
- You’re already selling into the EU and want AIMS documentation that can support — not substitute for — your EU AI Act work
You may have less immediate commercial reason to pursue certification when your AI use is limited to lower-risk internal productivity tools, no customer or diligence process has asked for certification, and your governance documentation is still being built out. Certification is an audit of an operating management system, not simply a documentation exercise — organizations should allow sufficient time to implement and actually operate their AIMS before the certification audit.
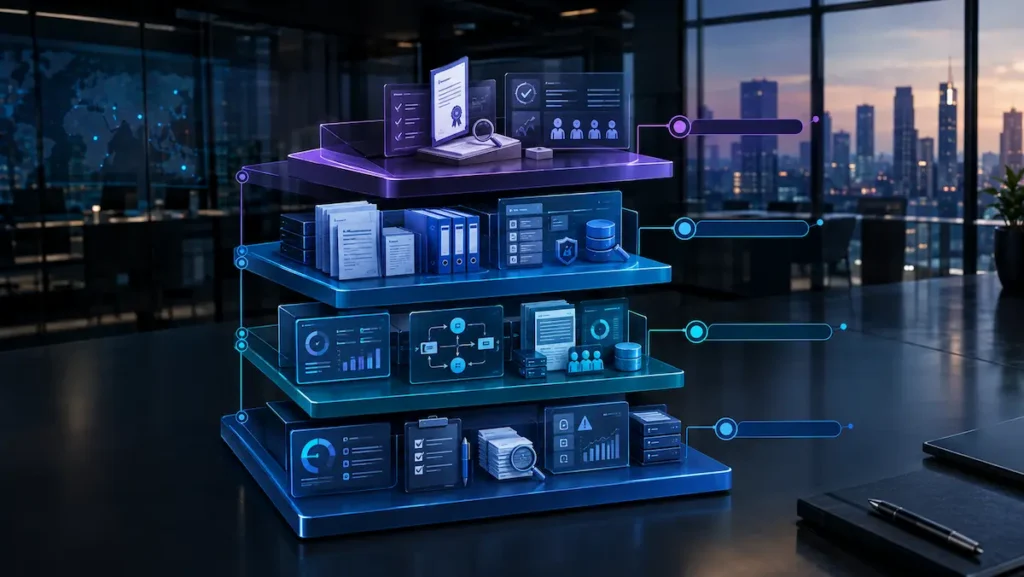
The ISO 42001 Readiness Stack™
| Layer | Key question | Output |
|---|---|---|
| 1. Gap Assessment | Where do we stand against Annex A today? | A scored gap list against the Annex A controls |
| 2. Documentation Mapping | What governance work do we already have? | Existing policies and assessments mapped to potential AIMS requirements |
| 3. Internal Audit & Governance Operations | Is the system actually operating, not just written? | Internal audit evidence, management review records |
| 4. Certification Audit Readiness | Are we ready for a third-party auditor? | Statement of Applicability, audit-ready evidence package |
Some organizations jump straight to certification preparation before completing Layers 1–3, which can turn certification into a scramble. Layer 2 in particular is where existing governance work pays off — it’s the step many generic certification guides skip past entirely.
Not sure how close your organization is to ISO 42001 readiness? Start with the AI Governance Readiness Assessment to identify documentation, risk-management, and operational gaps before building your certification plan.
Mapping Your Existing Governance Work to ISO 42001
If you’ve worked through TrusteraAI’s governance cluster already, you’re not starting from zero — though these are areas of potential alignment to explore with your own gap assessment, not one-to-one equivalences an auditor would simply accept at face value:
| Existing governance work | Potential ISO 42001 alignment |
|---|---|
| AI Policy Template | Clause 5.2 and related Annex A policy controls |
| AI Governance Checklist | Clauses 5.3, 7, and related governance controls |
| AI Risk Assessment Checklist | Clause 6.1 and related Annex A controls |
| AI DPIA Checklist | Clause 6.1.4 / Annex A.5 — where scope and methodology align |
| AI Vendor Risk Assessment | Potential alignment with Annex A.10 and related third-party/customer relationship requirements |
| AI Incident Response Plan | Potential alignment with applicable operational, performance-evaluation, and improvement requirements |
This isn’t a substitute for a real gap assessment — an auditor will want to see these operating consistently, with real records, not just documents on a shelf. But it means the gap assessment in Layer 1 is often smaller than founders expect once existing work is accounted for.
Annex A Is Not the Whole Standard
It’s easy to read an article like this and conclude that certification is simply “implement the applicable Annex A controls and you’re done.” It isn’t. Certification assesses conformity with the AIMS requirements in the standard’s main clauses — organizational context, leadership, policy, planning, risk and opportunity management, objectives, support, operation, performance evaluation, internal audit, management review, and continual improvement — in addition to whichever Annex A controls apply to your context. Annex A is the operational backbone, not the entire audit.
Annex A: The 38 Controls, Explained
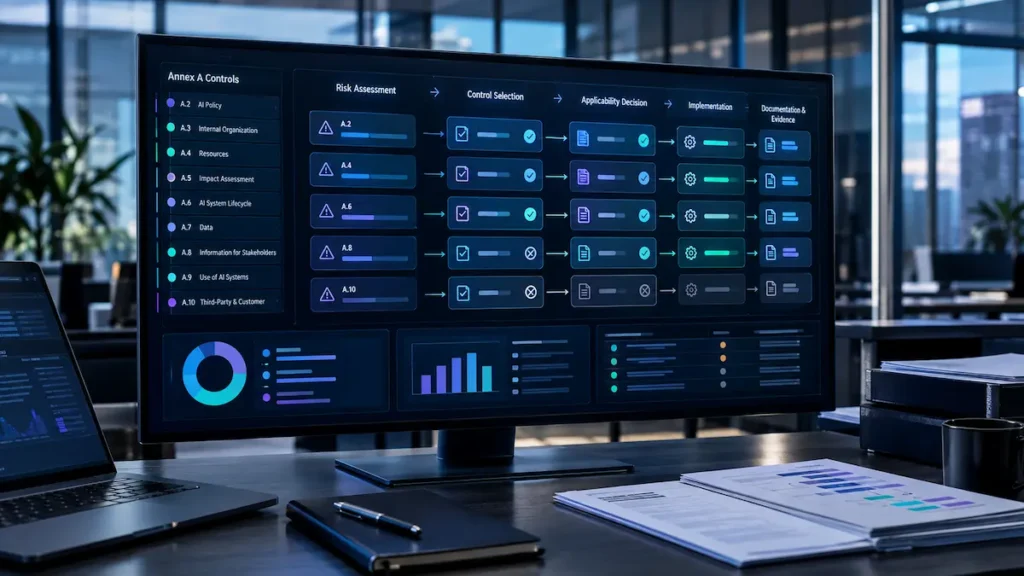
Annex A is a reference catalogue of 38 controls organized across nine control areas, numbered A.2 through A.10: AI policy, internal organization, resources for AI systems, AI impact assessment, the AI system lifecycle, data for AI systems, information for interested parties, use of AI systems, and third-party and customer relationships.
You don’t automatically implement every Annex A control in the same way. You determine the controls necessary to address your identified AI risks and risk-treatment decisions, compare them against Annex A, and document the resulting applicability decisions and justifications in your Statement of Applicability. The Statement of Applicability is a key audit document because it records which Annex A controls are applicable, how they’re addressed, and the justification for anything excluded.
For a small SaaS company with a limited AI footprint, the applicable controls will depend on its role, scope, AI systems, risks, and operating model — which is exactly why the gap assessment in Layer 1 matters more than memorizing every control.
What Auditors Actually Look For
Beyond the Statement of Applicability, certification auditors are generally looking for evidence that the management system is actually operating, not just documented:
- Evidence that the AIMS has been implemented and is operating effectively, rather than existing only as documented policies and procedures
- Internal audit results and how findings were addressed
- Management review records showing leadership engagement, not just a policy signed once
- Evidence that risk and impact assessments actually drove which controls were selected, rather than controls being picked first and justified after
- Clear ownership — who’s accountable for the AIMS, documented and consistent with how the organization actually operates
This is why Step 4 matters: a system that exists only on paper is unlikely to provide the implementation and performance evidence an external audit is designed to assess.
Cost & Timeline for a Lean SaaS Startup
Duration and cost vary significantly and depend on AIMS scope, organization size, number of AI systems in scope, existing management systems, documentation maturity, internal audit experience, and the certification body’s own process — so treat any specific number you see online, including here, as a planning scenario rather than an industry-standard figure.
- Readiness and gap assessment: internal effort, faster where governance groundwork already exists
- Documentation and internal audit: building or finalizing AIMS documentation and running at least one internal audit cycle before the external audit
- External certification audit: certification audits are generally conducted in two stages. Stage 1 evaluates readiness and the management system documentation; Stage 2 evaluates implementation and effectiveness, followed by surveillance and recertification activities under the certification body’s programme
- Total timeline: often measured in months rather than weeks; a narrowly scoped startup with mature governance may move faster, while a broader or newly built AIMS can take substantially longer
- Cost: driven primarily by AIMS scope, certification-body audit effort, organizational complexity, and any external implementation or consulting support
Request a quote from a certification body after defining your AIMS scope, rather than relying on generic online cost or timeline estimates.
Step-by-Step: Getting Certified
- Define your AIMS scope — which AI systems, products, or business units are actually in scope. Narrow scope keeps cost and timeline down.
- Run the gap assessment against the ISO/IEC 42001 requirements and applicable Annex A controls, accounting for governance work you already have.
- Close documentation gaps — write or finalize what’s missing (policy, risk assessments, impact assessments).
- Operate the AIMS — implement the system in practice and maintain evidence that its processes are operating effectively before the external audit.
- Run an internal audit and a management review before the external audit.
- Select a certification body and prepare for the two-stage external audit.
- Maintain it — certification isn’t one-and-done; surveillance audits and recertification follow on a recurring cycle.
Common Mistakes
- Treating Annex A as a checklist to implement top to bottom. It’s a reference set you select from and justify, not a mandatory list.
- Skipping the internal audit and jumping straight to the external one. Auditors notice a system that’s never been tested internally.
- Ignoring governance work you’ve already done. Rebuilding an AI policy from scratch when one already exists just adds cost and delay.
- Treating certification as a substitute for EU AI Act or GDPR compliance. It can support that work; it doesn’t replace it.
- Scoping too broadly on the first attempt. A narrow, well-run AIMS beats an ambitious one that isn’t actually operating yet.
FAQs
Is ISO 42001 for SaaS companies mandatory?
No. It’s a voluntary international standard. Nothing in EU or US law currently requires it, though specific customers, investors, or procurement processes may effectively expect it as a condition of doing business.
How is ISO 42001 different from SOC 2?
SOC 2 attests to defined controls — security, availability, confidentiality — a framework originating in the US. ISO 42001 certifies that an organization has a structured system for governing AI specifically. They address different governance concerns, so an organization may choose to pursue both depending on its customer requirements, risk profile, and assurance objectives.
Does ISO 42001 satisfy EU AI Act requirements?
Not automatically. The EU AI Act is binding law with its own obligations tied to provider or deployer status and risk classification, and the European Commission has noted that ISO 42001 isn’t aligned with the Act’s specific quality-management-system requirements. ISO 42001’s documentation can support AI Act work but doesn’t constitute legal compliance on its own.
How long does ISO 42001 certification take for a startup?
It varies significantly by scope and organizational maturity — often measured in months rather than weeks. Get a specific estimate from a certification body once you’ve defined your AIMS scope rather than relying on a generic timeline.
Do I need to implement all 38 Annex A controls?
No. Annex A is a reference catalogue. You determine which controls are applicable to your context based on your own risk and impact assessments, and document your inclusions, exclusions, and justification in a Statement of Applicability.
Is ISO 42001 the same as an AI certification?
No. ISO/IEC 42001 is a management-system standard. Certification evaluates whether an organization’s AIMS conforms to the standard within the certified scope — it does not certify that an individual AI model is accurate, safe, unbiased, or legally compliant.
Related Resources
- AI Governance Checklist for SaaS — the pillar this fits under
- AI Policy Template — potential alignment with AIMS policy documentation
- AI Risk Assessment Checklist — potential alignment with Clause 6.1
- AI Vendor Risk Assessment — potential alignment with Annex A.10
- AI DPIA Checklist for Spain-Facing SaaS Startups — potential alignment with Annex A.5
- AI Incident Response Plan — potential alignment with applicable operational requirements
Sources:
- ISO/IEC 42001:2023 — AI management systems
- ISO/IEC 42006:2025 — Requirements for bodies providing audit and certification of AI management systems
- European Commission — Standardisation of the AI Act
- European Commission — Understanding the standardisation of the AI Act (FAQ)
- EUR-Lex — Regulation (EU) 2024/1689 (Artificial Intelligence Act)
This article provides general educational information and is not a substitute for guidance from a certification body or qualified legal counsel. Verify current requirements directly with ISO and an accredited certification body before starting a certification project.